Yes, a modern CMMS can enforce secure, role-based contractor access when it is paired with document-driven workflows and integration into your physical access control system. The mechanism combines role-based permissions, time-bound certifications, and automatic enforcement at the gate or turnstile. Done correctly, it blocks non-compliant contractors before they reach a work site and leaves an audit trail behind every entry decision. The sections below outline what to require, test, and monitor.
TL;DR:
- Ensuring contractor access is role-based and time-bound prevents permission creep and automates revocation tied to work orders or permits.
- Integrating the CMMS with physical access control systems allows real-time enforcement, immediate permit revocation, and maintains an audit trail.
- Contractor onboarding must include document verification, accreditation, site-specific inductions, and automated status updates to avoid reliance on manual checks.
- Multi-site management separates central policy setting from site-specific application, with dashboards to monitor compliance and expiring credentials across locations.
- Testing integrations under failure conditions before deployment is crucial to ensure real-time enforcement and accurate compliance status verification.
Table of Contents
- Role-based access control (RBAC) for contractors: what facility managers must know
- Integration with physical access control systems and permit-to-work systems
- Contractor onboarding, document tracking, and compliance workflows inside a CMMS
- Multi-site visibility and site-level permissions: scaling contractor access across locations
- Implementation checklist: what to require when you spec a CMMS for contractor access control
- Why MPulse supports contractor access control
- Case studies and examples of effective contractor access control
- Regulatory compliance considerations for contractor access control
- How contractor access control affects overall facility security posture
- Author perspective: practical priorities and immediate next steps
- How MPulse can help with contractor access control
- Sources
- FAQ
Role-based access control (RBAC) for contractors: what facility managers must know
Role-based access control assigns permissions according to job function rather than individual identity, so a contractor’s access reflects what their work actually requires. The NIST RBAC project formalizes this model and ties it directly to the principle of least privilege: contractors should hold only the access needed for a specific task and time window, never blanket “vendor” privileges that persist indefinitely.
For facility teams, this means mapping each contractor role to a defined set of work-order types, physical areas, and time windows rather than issuing generic badges. An HVAC technician scheduled for a rooftop unit repair needs roof access and mechanical room entry for the duration of that work order, nothing more. A roles engineer who only supports a single project should never carry the same standing access as a facility’s long-term maintenance partner.
Common role definitions include:
- Scheduled maintenance contractor: access limited to specific equipment zones during assigned shift windows.
- Emergency response contractor: broader temporary access triggered by an incident ticket, expiring automatically once the ticket closes.
- Project-based contractor: access scoped to a defined jobsite area for the life of a capital project, with a hard expiration date.
- Inspector or auditor: read-only or escorted access tied to a single visit.
The biggest operational risk is permission creep: access granted for a short job that never gets revoked. The fix is dynamic expiration tied to the work order or contract end date, not a manual deprovisioning step that depends on someone remembering to act. Periodic access audits catch what automation misses, particularly for contractors who move between multiple active work orders.
Pro Tip: Set every contractor role to expire by default and require an explicit renewal step, rather than defaulting to open-ended access that someone has to remember to close.
Integration with physical access control systems and permit-to-work systems
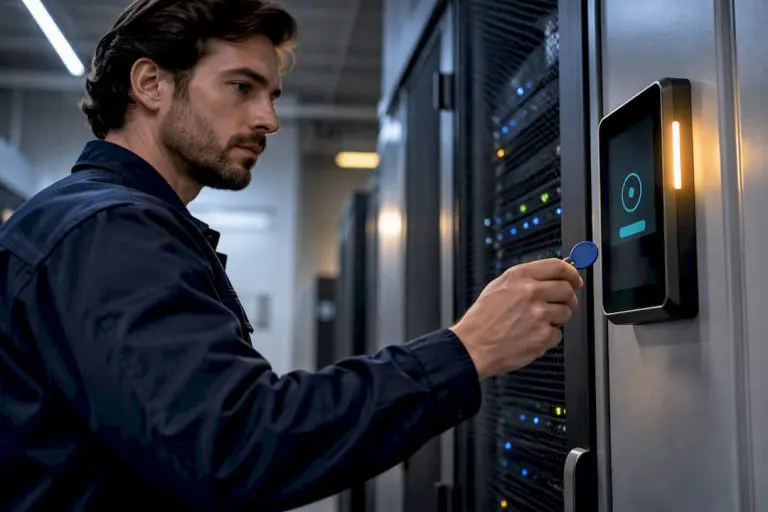
A CMMS that tracks compliance status is only half the solution. The other half involves making that status actionable at the door, which requires integration between the CMMS and the facility’s physical access control system (PACS). This is typically handled through APIs or webhooks that exchange a small set of fields in real time.
- Permit ID: links a specific work authorization to a specific entry event.
- Authorized entrants list: the exact set of individuals cleared for that permit.
- Validity window: the start and end time the permit remains active.
- Compliance flags: certification, insurance, or induction status that must be current for entry to succeed.
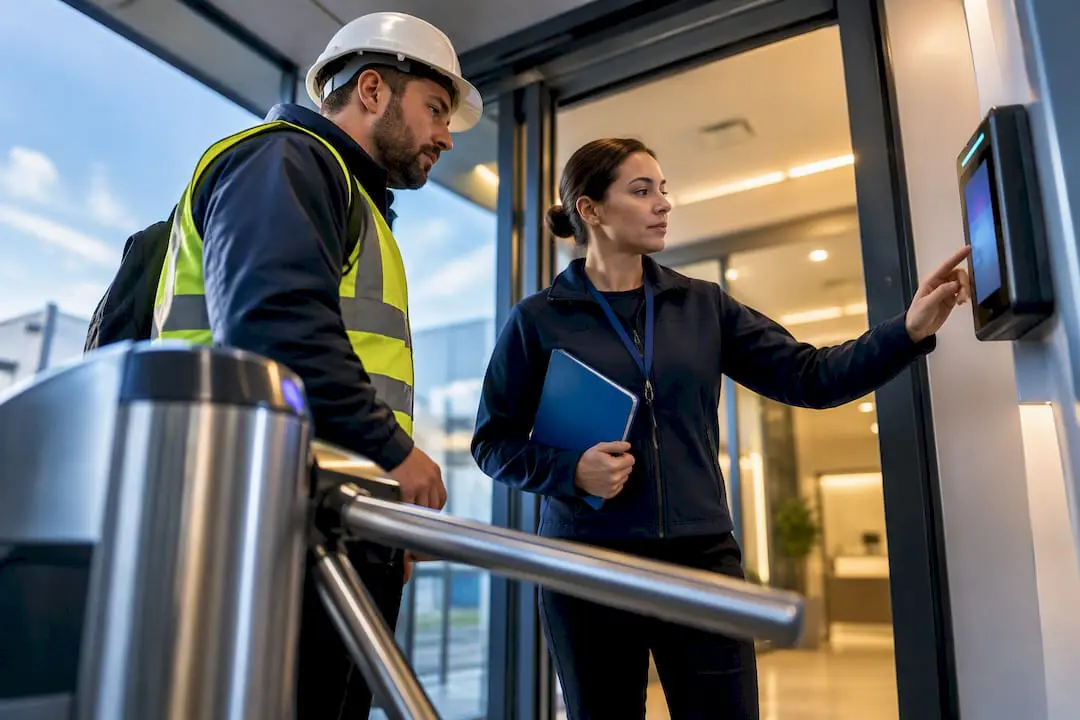
When a permit is revoked or a certification lapses, that change needs to reflect at the PACS immediately, not at the next manual sync. Facilities with limited connectivity should also plan for offline or edge-capable check-in devices that cache the last known compliance state and reconcile once connectivity returns, since a false positive at a turnstile is a safety failure, not just an inconvenience.
This integration pattern also supports OSHA’s permit-required confined spaces rules, which require documented entry permits, authorized entrant lists, and retained records of canceled permits. Tying CMMS permit data directly to PACS logs gives facility teams both the entry control and the audit-ready paper trail in one system, and it supports accurate evacuation accounting during a drill or an actual emergency. Before going live, test the integration under failure conditions: a revoked permit, an expired badge attempt, and a network outage should all produce predictable, safe outcomes.
Contractor onboarding, document tracking, and compliance workflows inside a CMMS
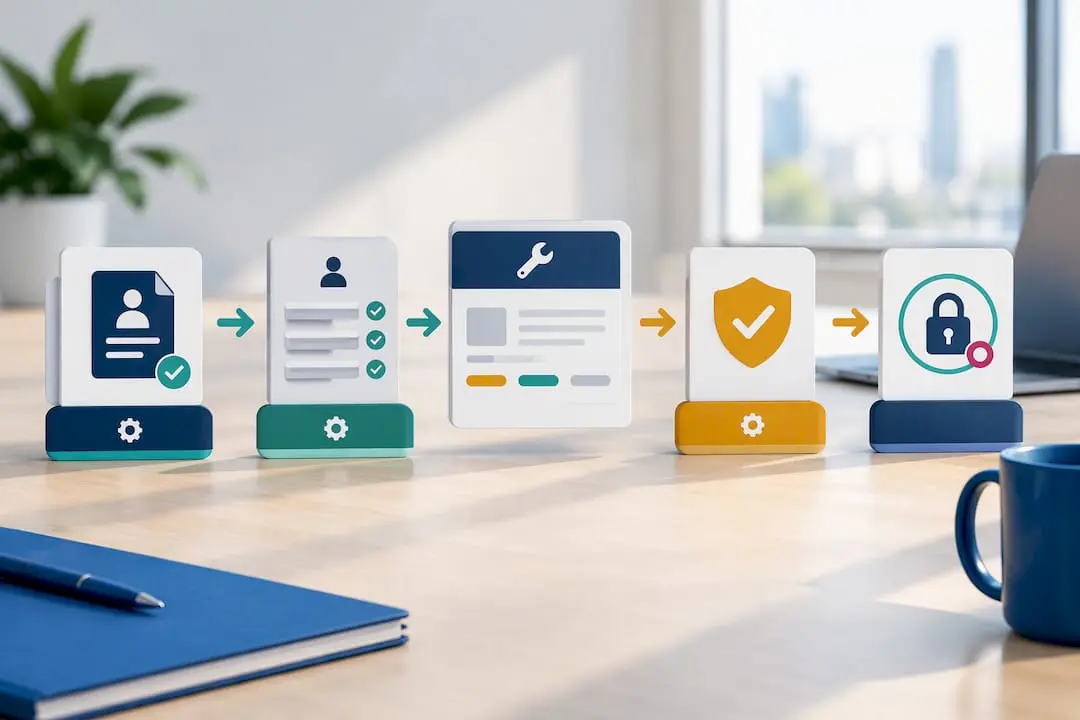
Access control is only as reliable as the onboarding process feeding it. A contractor should never receive site access until their documentation clears a defined checklist inside the CMMS.
- Company profile and worker roster: the contracting firm’s registration details and a current list of individual workers.
- Insurance and licensing documents: uploaded, dated, and set to trigger a review before expiration.
- Certifications and qualifications: confined space, working at height, electrical, or other task-specific credentials tied to the roles they’ll be assigned.
- Site induction completion: confirmation that safety orientation has been completed for this facility specifically.
- Approval sign-off: a named site admin who authorizes the final access grant.
Each contractor record should move through defined states: compliant, expiring, non-compliant, and blocked, with the transition from expiring to blocked happening automatically as documents pass their validity date. This removes the dependency on someone manually checking a spreadsheet before every shift.
Documents and approvals should attach to specific work orders rather than sitting as a general company file, so that a contractor’s access rights track the actual job they were cleared for. A useful delegation model splits administration between the contractor company’s own admin, who manages their workers’ records and uploads, and the site admin, who approves access and sets the boundaries of what that access covers. This division reduces the administrative load on facility staff while keeping approval authority where it belongs. For a deeper walkthrough of onboarding structure, see this contractor onboarding guide.
Multi-site visibility and site-level permissions: scaling contractor access across locations
Organizations managing more than one facility need a structure that keeps policy consistent without forcing every access decision through a central bottleneck. The typical pattern separates central administrators, who set organization-wide rules such as required certifications and default expiration periods, from site administrators, who apply those rules to their own location and approve or deny specific access requests.
- Role scoping by site: a contractor role defined centrally can be restricted to one location or a defined subset of facilities.
- Asset-area restrictions: permissions can be narrowed further to specific buildings, floors, or equipment zones within a site.
- Temporary project exceptions: a site admin can grant a time-limited exception for a capital project without altering the contractor’s standing role.
- Cross-site contractor scenarios: a contractor working across multiple locations needs a single identity record that carries different access rights per site, rather than duplicate profiles that drift out of sync.
For portfolios with many locations, dashboards tracking contractor compliance rates, expiring certifications, and open work orders by site give facility leadership a real-time view of exposure across the organization. Analyst research on the asset management software market notes that enterprise buyers increasingly prioritize consolidated platforms with deeper integrations as they scale contractor and asset management across multiple sites, rather than managing access separately at each location.
Implementation checklist: what to require when you spec a CMMS for contractor access control
When evaluating a CMMS for contractor access control, test it against specific, verifiable requirements rather than a vendor’s feature list.
- Role-based access control with least-privilege defaults, matching the approach the NIST RBAC standard describes.
- Time-bound access that expires automatically with the underlying work order, permit, or certification.
- An API or webhook connection to your PACS capable of real-time permit and revocation updates.
- Audit logs covering every access grant, denial, and administrative change, with timestamps and the responsible user.
- Expiry automation that moves a contractor record through compliant, expiring, non-compliant, and blocked states without manual intervention.
- Encrypted data handling for stored documents and credentials, along with admin-level audit trails for who accessed what.
During a demo, ask the vendor to run three operational tests live: revoke a permit and confirm the PACS reflects it immediately, attempt entry with an expired certification and confirm the system blocks it, and simulate an offline check-in to see how the system reconciles once connectivity returns. Also confirm mobile check-in support, contractor self-service for document uploads, and a stated service-level commitment for integration support. The components overview is a useful reference point for understanding how these pieces typically connect within a CMMS architecture.
Pro Tip: Ask for a live permit-revocation test during the demo, not a slide describing the feature. It’s the fastest way to see whether enforcement is actually real-time.
Why MPulse supports contractor access control
MPulse CMMS includes role-based access control built around the same least-privilege approach outlined above, letting facility teams assign contractor permissions by job function and time window rather than by blanket vendor status.
- MPulse cites efficiency improvements among users but does not specify exact figures in this context.
- The platform offers integration capabilities relevant for teams linking CMMS compliance data to PACS enforcement.
- Add-on options include a DataLink Integration Adapter and Single Sign On for organizations building out integration and identity management around contractor access.
- Further reading on feature requirements is available in this CMMS features overview and this piece on CMMS and regulatory compliance.
These are MPulse’s own published figures and claims, offered here as reference points for evaluating fit against the checklist above.
Case studies and examples of effective contractor access control
The clearest examples of effective contractor access control come from facilities that tie compliance status directly to physical entry decisions rather than relying on manual checks at the gate. Contractor access platforms in this space describe an enforcement model where a badge or turnstile denies entry the moment a certification lapses or a permit closes, without a security guard needing to check a spreadsheet first. Vendor implementations in this category typically combine automated induction tracking, document verification, and real-time PACS enforcement to keep non-compliant workers off site before an incident occurs.
Similar patterns appear in contractor management platforms built specifically around access control, which pair automated document checking with rules that block entry the instant a required credential expires. The common thread across these examples is not a specific software brand. It is the shift from periodic manual review to continuous, automated enforcement, which closes the gap between when a contractor becomes non-compliant and when that status actually affects their ability to get on site. Facility teams evaluating a CMMS for this purpose should look for the same pattern: compliance state and physical access decisions connected in real time, not reconciled at the end of the week.
Regulatory compliance considerations for contractor access control
Contractor access control intersects with regulatory requirements most directly around permit-to-work processes. OSHA’s standard for permit-required confined spaces requires documented entry permits, a list of authorized entrants, and retention of canceled permits, which makes contractor access a compliance obligation rather than a purely operational preference in these contexts. A CMMS that generates and stores this documentation automatically, tied to the actual access event, gives facility teams a defensible record if an inspector asks for evidence.
Beyond confined space work, facilities operating under process safety management or similar high-hazard frameworks face comparable documentation expectations for contractor entry and oversight. The specific requirements vary by industry and jurisdiction, so facility managers should confirm applicable rules with their compliance officer or a qualified safety professional rather than relying on general guidance. What a CMMS can reliably provide is the infrastructure: automated permit generation, expiration tracking, and audit logs that make demonstrating compliance far less labor-intensive than reconstructing records after the fact.
How contractor access control affects overall facility security posture
Contractor access is frequently the weakest point in a facility’s security posture, not because contractors are inherently a risk, but because their access tends to be granted informally and revoked inconsistently. A facility that enforces role-based, time-bound access for contractors closes a gap that standing employee access controls don’t address, since employee turnover and access reviews typically follow much more structured processes.
The security benefit compounds across a portfolio. When contractor compliance status feeds directly into PACS enforcement, a facility gains a consistent record of who was on site, under what authorization, and for how long, which matters as much for evacuation accounting during an emergency as it does for routine security review. Facilities without this integration tend to rely on paper sign-in sheets or informal badge issuance, which creates blind spots that are difficult to reconstruct after an incident. Treating contractor access as a core part of the security architecture, rather than an administrative afterthought, is one of the more direct improvements a facility team can make to its overall security posture without new hardware investment.
Author perspective: practical priorities and immediate next steps
The fastest wins here are unglamorous: map every contractor role to actual permit and work-order data, make expiration automatic rather than manual, and test permit revocation against your PACS before you trust it in production. Teams running a pilot should focus on the failure cases, not the happy path. Confirm details against your compliance officer and vendor documentation before rolling out broadly.
— Mark
How MPulse can help with contractor access control
If you’re mapping the requirements above against your current CMMS and finding gaps, MPulse’s pricing page outlines the Professional and Advanced plans, along with Technician License options for facility teams onboarding contractor users specifically.
MPulse also offers implementation services, including support for integrating with existing PACS setups and configuring role-based permissions during setup, so your team isn’t building this from scratch. A consultation is a reasonable next step if you want a specific answer on integration scope before committing.
Sources
- Role Based Access Control | CSRC
- OSHA permit-required confined spaces rules (1926.1206)
- Spring 2024 Asset Management Software Reports: A Summary
- Contractor Access Control Software | Twind
FAQ
What are the most popular CMMS platforms?
Market rankings for CMMS and EAM software show a stable set of top vendors, though adoption and return on investment vary by category and organization size. The right fit depends more on integration needs and compliance requirements than on general popularity.
Does SAP have a CMMS system?
SAP offers enterprise asset management functionality through its broader ERP suite, which some organizations use for maintenance management alongside or instead of a dedicated CMMS. Whether that approach fits depends on whether a facility needs a standalone maintenance-focused tool or already runs SAP for other enterprise functions.
Where does a CMMS collect its data from?
A CMMS typically pulls data from work orders, asset records, preventive maintenance schedules, inventory logs, and increasingly from integrations with sensors, ERPs, and access control systems. For contractor access specifically, data also comes from onboarding documents, certifications, and permit records tied to each work order.
What is the purpose of CMMS software?
CMMS software centralizes maintenance operations, including work order management, preventive maintenance scheduling, asset tracking, and inventory control, so facility teams can reduce unplanned downtime and keep accurate compliance records. For contractor management specifically, it adds role-based access control and document tracking so only qualified, compliant workers can access a site.